

Subscribe to CERT Mailing Lists
43.8188277,11.1949099
Via Bruno Benedetto Rossi 1
Sesto Fiorentino
50019, Firenze

Manager
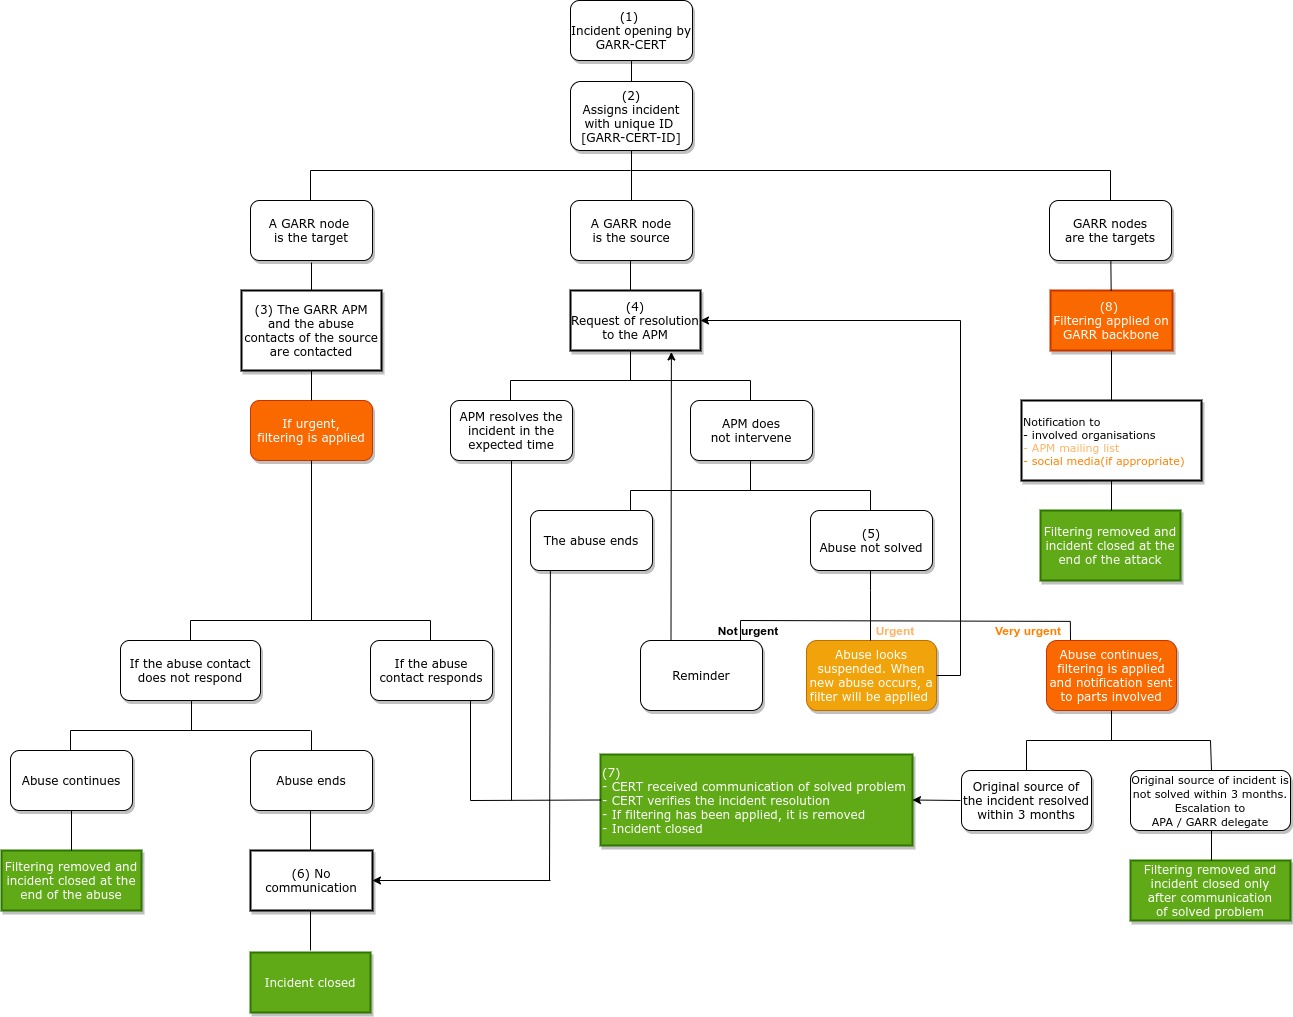
Procedura Approvata dal CTS GARR il 17/6/2020
sostituisce Procedura gestione incidenti 23-01-2007
Here you will find the GARR-CERT procedure for the management of security incidents involving GARR
Foreword
Contacts for security incidents
Each organisation connected to GARR network must appoint a local technical contact point, the APM (Access Port Manager). The APM manages the connection with GARR network and is technical liaison between the organisation and GARR also for the management of security incidents. The APM definition is available on the GARR institutional website.
Communications
Communication between GARR-CERT and involved organisations are usually performed via digitally signed e-mails
Protection from distributed external attacks
Since October 2019, GARR network is equipped with an automatic system for the mitigation of some types of external attacks, which are distributed and aimed at creating disservices (DDoS - Distributed Denial of Service). This system is based on Corero|Juniper technology. When some indicators exceed the threshold values, the network devices react and selectively eliminate the traffic corresponding to this type of attack by applying temporary filters, thus allowing the individual nodes to maintain normal network functionality. The procedure is automatic, without any user intervention. The indicators to be used and the respective threshold values are configured by GARR-NOC.
Filtering
In some special cases, incident management involves filtering one or more network addresses on routers managed by GARR. We would like to emphasize that the application of these filters is always intended to protect and safeguard the functionality of the network and the connectivity services available to users of the GARR network. In the most evident case in which GARR IPs are the direct or indirect targets of an external attacke, the request for intervation of filtering by CERT/NOC often comes from users (APMs) themselves, asking to recover access to their devices and possibly intervene on their configurations in order to mitigate the problem also at the local level. In the event that GARR IPs are clearly the source of illicit traffic and there is no response from the APM in the expected times, the IPs involved are filtered by GARR (with the criteria described in the security incident management procedure), in order to protect its users and prevent any possible legal consequences. Three months after the filtering, in the absence of a response from the APM, GARR will proceed to inform the APA and the GARR Delegate of the competent Authority (escalation).
Types of incidents currently treated (with indication of the incident response time)
Depending on the type, below are listed the expected time required for the APM to resolve the incident starting from the notification. In case the APM needs more time to resolve the incident, it is necessary to make an explicit request to GARR-CERT.
Even outside the NOC and CERT operating hours, In the event of an incident which significantly impacts user connectivity, such as a distributed SYNFlood, the managers of GARR-NOC and CERT decide how to:
Other cases that expose users to serious security problems, for example in the case of ongoing data breaches involving particular data, can also be treated as a precaution as in the previous point (a).
The updating of GARR Security Incident Management Procedure is due, in addition to the evolution of the types of threats to the network and user systems, also to the evolution of the regulations in force in Italy related to cybercrime.
Before the recent directives contained in the Minimum Security Measures for the Public Administration (AgID, 26/4/2016 - https://www.agid.gov.it/it/sicurezza/misure-minime-sicurezza-ict) and transposition in Italy of the European Regulation for the Protection of Personal Data (Legislative Decree 101/2018 - https://www.garanteprivacy.it/web/guest/provvedimenti/provvedimenti-a-carattere-generale), cybercrime appears for the first time in Italy with Law 547 of 1993, which introduces changes and additions to the Criminal Code and the Criminal Procedure Code regarding cybercrime.
These are, to date, the cybercrimes punished by the Italian Penal Code (Courtesy Translation):

Servizio GARR CERT
https://www.cert.garr.it
Ai sensi degli artt. 13 e 14 del Regolamento UE 679/2016, l’associazione riconosciuta senza scopo di lucro Consortium GARR con sede in via dei Tizii, 6 - 00185 - Roma - Italia, è il Titolare del trattamento dei Suoi dati personali. I dati personali acquisiti formano oggetto di trattamento nel rispetto della normativa sopra richiamata. In relazione ai suddetti trattamenti il Titolare fornisce le seguenti informazioni:
Il Consortium GARR
tel: +39 4962 2000
contatto mail:
Dott. Giorgio Valente
tel: +39 4962 2057
contatto mail:
Consortium GARR con sede in via dei Tizii, 6 - 00185 - Roma - Italia
I sistemi informatici e gli applicativi dedicati al funzionamento di questo sito web rilevano, nel corso del loro normale funzionamento, alcuni dati (la cui trasmissione è implicita nell'uso dei protocolli di comunicazione di Internet) non associati a utenti direttamente identificabili.
Tali informazioni - che per loro natura potrebbero, attraverso elaborazioni ed associazioni con dati detenuti da terzi, consentire l'identificazione degli utenti - non sono raccolte per essere associate a interessati identificati. Questi dati vengono utilizzati al solo fine di ricavare informazioni statistiche anonime sull'uso del sito e per controllarne il corretto funzionamento. I dati potrebbero essere utilizzati per l'accertamento di responsabilità in caso di compimento di reati informatici o di atti di danneggiamento del sito; salva questa eventualità, allo stato i dati sui contatti web non persistono oltre il tempo necessario all' effettuazione delle verifiche dirette a garantire la costante sicurezza del sistema.
I dati forniti dall'utente all'atto della registrazione (Nome, Cognome, Username, password, indirizzo e-mail, Istituto/Ente di appartenenza) vengono custoditi fino a quando si estingue il rapporto di utenza. Il Consortium GARR non svolge attività di profilazione degli Utenti.
Per informazioni sull'uso dei cookies fare riferimento all'informativa dedicata:
Il Consortium GARR effettua trattamenti di dati personali nei limiti di quanto ciò sia strettamente necessario allo svolgimento delle proprie funzioni istituzionali, escludendo il trattamento quando le finalità perseguite possono essere realizzate mediante dati anonimi o modalità che permettono di identificare l'interessato/utente solo in caso di necessità.
Le particolari finalità, relative a singoli servizi o comunque a specifici trattamenti, sono evidenziate in maniera dettagliata nelle informative privacy relative ai singoli servizi e nei vari canali tematici di accesso. All'interno di essi l'utente potrà eventualmente trovare informazioni integrative sul trattamento dei dati personali.
I dati saranno trattati per tutto il tempo necessario allo svolgimento del rapporto in essere e comunque per il tempo richiesto dalla normativa italiana in vigore.
Salvo quanto specificato per i dati di navigazione, l'utente è libero di fornire i dati personali riportati nei moduli di richiesta per sollecitare l'invio di materiale informativo o di altre comunicazioni. Il loro mancato conferimento può comportare l'impossibilità di ottenere quanto richiesto.
I dati personali verranno trattati in forma cartacea, informatizzata e telematica ed inseriti nelle pertinenti banche dati cui potranno accedere, e quindi venirne a conoscenza, gli operatori espressamente designati dal Titolare quali Incaricati del Trattamento dei dati personali, che hanno assunto un esplicito obbligo di riservatezza, i quali potranno effettuare operazioni di trattamento nel rispetto delle disposizioni di legge necessarie a curare, oltre alla riservatezza, l’integrità, la sicurezza, l'aggiornamento e la pertinenza dei dati nel rispetto alle finalità dichiarate.
I dati raccolti sono inerenti essenzialmente a:
Dati identificativi: indirizzo IP ed ove conferito: nome e cognome, e-mail delle persone fisiche; i dati forniti dall’interessato possono essere raccolti presso eventuali contitolari e/o Responsabili del trattamento per conto del Consortium GARR.
I dati personali degli utenti sono utilizzati unicamente al fine di eseguire il servizio o la prestazione richiesta e sono comunicati a terzi nei soli casi in cui:
In relazione ai predetti trattamenti potranno essere da Lei esercitati i diritti di cui agli artt. da 15 a 22 GDPR, quali:
Per l’esercizio dei propri diritti l’interessato può rivolgere la propria istanza al Consortium GARR, Via dei Tizii, 6, 00185 - Roma, telefonando al numero +39 0649622000, mandando un fax al numero +39 0649622044 o inviando una mail all'indirizzo
La sottoscrizione della presente comunicazione deve intendersi quale consenso espresso al trattamento dei Suoi dati personali.
Ulteriori informazioni circa il trattamento dei dati potranno essere comunicate anche verbalmente.

-----BEGIN PGP SIGNED MESSAGE-----
Hash: SHA256
1. Document Information
1.1 Date of Last Update
Version 1.2, published 26 June 2003.
Version 1.3, published 25 May 2022.
1.2 Distribution List for Notifications
Notifications of updates are submitted to the mailing list (in
Italian):
This email address is being protected from spambots. You need JavaScript enabled to view it.
1.3 Locations where this Document May Be Found
The current version of this document is available from the GARR-CERT
WWW site:
https://www.cert.garr.it/en/about/rfc-2350
1.4 Authentication of this document
This document has been signed with the GARR-CERT PGP Master Key.
1.5 Revision History
1.0 - First release.
1.1 - New address and phone number.
1.2 - New phone numbers.
1.3 - New links, drop of fax number, new phone numbers.
2. Contact Information
2.1 Name of the Team
GARR-CERT: the GARR Network Computer Emergency Response Team.
2.2 Address
GARR-CERT c/o
INFN, Sezione di Firenze
Servizio Calcolo e Reti
Via G. Sansone 1
I 50019 Sesto Fiorentino (FI)
ITALY
2.3 Time Zone
Central European (GMT+0100 and GMT+0200 from the last Sunday of
March to the last Sunday of October).
2.4 Telephone Number
+39 055 4572053
+39 055 4572723
+39 055 4572724
2.5 Other Telecommunication
None available.
2.6 Electronic Mail Address
This email address is being protected from spambots. You need JavaScript enabled to view it.
Messages sent to this address are received by all GARR-CERT members.
2.7 Public Keys and Encryption Information
GARR-CERT has a PGP Master Key, used to sign GARR-CERT's official
documents (including this one):
pub 1024/65126042 2009/07/03 GARR-CERT Master Key <This email address is being protected from spambots. You need JavaScript enabled to view it. >
Fingerprint: C6A5 D891 E4CA ACB5 A701 1876 C19C 4C93 6512 6042
It can be found at the GARR-CERT PGP page or at the PGP Public Key
Servers.
Details on the PGP keys of GARR-CERT members can be found at:
https://www.cert.garr.it/en/pgp-en/pgp-keys-info
2.8 Team Members
Leonardo Lanzi, of University of Florence, is the GARR-CERT
coordinator. The other team members are listed at:
https://www.cert.garr.it/en/about/team
2.9 Other Information
General information (in Italian) about GARR-CERT can be found at:
https://www.cert.garr.it/
2.10 Points of Customer Contact
GARR-CERT can be contacted:
- via e-mail at: This email address is being protected from spambots. You need JavaScript enabled to view it.
- by telephone (Mon-Fri, 8.00-17:00);
- by web using the form mentioned in Section 6.
3. Charter
3.1 Mission Statement
The purposes of GARR-CERT are:
- to assist the users of the GARR Networkin implementing
proactive measures to reduce the risk of computer security
incidents;
- to assist the users of the GARR network in responding to such
incidents when they occur.
3.2 Constituency
The GARR-CERT constituency is the community of the users of the GARR
Network, the Italian Academic and Research Network.
3.3 Sponsorship
GARR-CERT is an operative service of the GARR Consortium.
3.4 Authority
GARR-CERT operates under the auspices of the GARR members and the
supervision of the GARR Consortium management.
In case of missing support from the local APM, it has authority to
obtain from GARR NOC the filtering of the involved node(s) on the
GARR network border routers.
4. Policies
4.1 Types of Incidents and Level of Support
GARR-CERT is authorized to address all types of computer security
incidents that occur at nodes connected to the GARR network.
The level of support given by GARR-CERT will vary according to the
severity of the incident and the GARR-CERT's resources at the time.
Every effort will be done to give some response within one working
day.
No direct support will be given to end-users, as they are expected
to contact their system administrators.
GARR-CERT expects that the APM of the sites involved in security
incidents will cooperate in the resolution of the problem.
The incident handling procedure, which, in extreme cases, will lead
to filtering the compromised node(s) on the GARR network border
routers can be found at:
https://www.cert.garr.it/en/incidents-management/management-procedure
GARR-CERT is committed to keeping its constituency informed of
potential vulnerabilities, possibly before they are actively
exploited.
4.2 Co-operation, Interaction and Disclosure of Information
GARR-CERT, unless explicitly authorized, will not divulge the
identity of nodes victims of computer security incidents.
4.3 Communication and Authentication
Telephone and unencrypted e-mail are considered sufficient for the
transmission of low-sensitivity data.
If it is necessary to send high sensitivity data by e-mail, PGP will
be used.
Network file transfers will be considered similar to e-mail for
these purposes.
5. Services
5.1 Incident Response
GARR-CERT will help system administrators of nodes connected to the
GARR network in handling computer security incidents.
In particular:
- investigating the nature and extent of the incident;
- determining the initial cause (e.g. vulnerability exploited);
- keeping contacts with other sites involved;
- reporting to other CSIRTs;
- helping in removing the vulnerability.
To make use of GARR-CERT's incident response services, please use
the methods listed in Section 2.10.
5.2 Proactive Activities
GARR-CERT coordinates and maintains the following services to the
extent possible depending on its resources:
- mailing lists.
- auditing services;
- dissemination of information about vulnerabilities and
recommended security measures;
- testing and developing security tools.
6. Incident Reporting Forms
If possible, use the following form to report a security incident:
https://www.cert.garr.it/en/incidents-management/reports-accidents
7. Disclaimers
While every precaution will be taken in the preparation of
information, notification and alerts, GARR-CERT assumes no
responsibility for errors or omissions, or for damages resulting
fron the use of the information contained within.
-----BEGIN PGP SIGNATURE-----
Version: GnuPG v1
iEYEAREIAAYFAmKPQlsACgkQwZxMk2USYEK3kgCgxucqtRXqpcVPSU8/NzDmf8Sm
w+AAn0t1I5pi8dR6N1alXBFxx0uv/ViS
=8rjs
-----END PGP SIGNATURE-----